

I Build, Test
& Analyse
Security
Across Systems and Networks
0 +
Years of experience
0 +
Security projects
Cybersecurity researcher
focused on penetration testing,
vulnerability research & web security
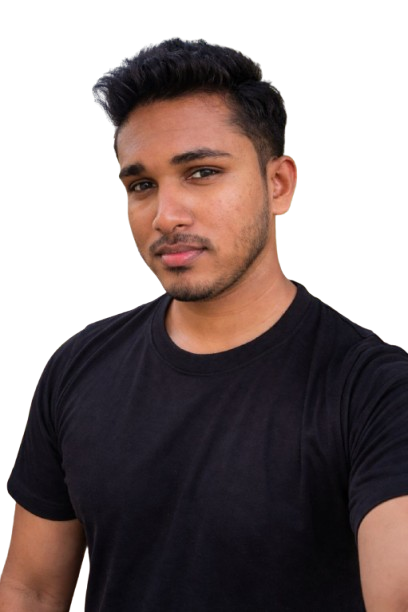
I'm Ameesha Heshan [Nova Exzzr] - a cybersecurity professional and student
from Sri Lanka with hands-on experience across penetration
testing, web application security, API security, network
security and security research.
With a strong foundation in Linux environments, network security,
and security infrastructure, I bring an engineering-focused
perspective when assessing systems. Combining practical
programming and scripting skills with deep knowledge of
system internals and network protocols allows me to analyze
both application logic and infrastructure attack surfaces.
I’m particularly driven by understanding how vulnerabilities
exist, how attacks operate across systems, and how technology
can be engineered with resilience from the ground up.
I continuously develop through cybersecurity labs,
independent research, personal security projects and
hands-on experimentation with offensive security tools and
techniques.
nova@sec-lab:~$ whoami
Ameesha Heshan [Nova Exzzr] — Penetration Tester & Security Researcher
nova@sec-lab:~$ cat /etc/security_profile.conf
- [+] Primary Environments: Kali Linux, Debian, Arch Linux, Docker
- [+] Core Arsenal: Burp Suite Pro, Nmap, Wireshark, Metasploit, Sqlmap, Gobuster
- [+] Offensive Security: Web & API Penetration Testing, OWASP Top 10, Vuln Assessment
- [+] Network & Defense: Threat Hunting, Packet Analysis, TCP/IP, Firewall & System Hardening
- [+] Programming & Scripting: Python (Exploits & Automation), Bash, PHP, JavaScript
- [+] Platforms & Practice: TryHackMe, HackTheBox, PortSwigger Web Security Academy
- [+] Credentials: Cisco Certified (CyberOps, Network Defense, Networking Basics)
- [+] Current Status: Available for Security Audits, Pentesting & Research
nova@sec-lab:~$ ./run_audit.sh --target all --stealth█
2023 - Present
SUGOI International - Junior Software Engineer | Task Automation
System Support, System Security, Automation, Development
Provided system support, Sofware Security Test, Task Automation and Product Development. Troubleshot and resolved issues in business-critical applications to smooth operations. Monitored and enforced Production security and protocols. Handled network troubleshooting in Company Intranet and Extranet. Contributed to increased operational efficiency through responsive and strategic IT solutions.
2022 - 2023
Ceylon Leisure Travels Pvt Ltd.
Web Developer ( Coded / CMS)
Developed responsive and user-friendly websites using HTML, CSS, PHP, MySQL, Laraval, bootstrap and WordPress. Designed and implemented custom WordPress themes and plugins tailored to client needs. Conducted regular manual testing to ensure functionality, performance, and user experience. Focused on website security, performing checks to identify and resolve vulnerabilities. Ensured websites were stable, secure, and free from critical flaws through ongoing maintenance and testing.
2022 - 2023
Xpert Solutionz Pvt Ltd.
Web Developer
Designed and developed user-friendly websites using WordPress Shopify. Conducted manual testing to identify and resolve functional and security issues. Ensured website security and stability through regular vulnerability assessments. Maintained overall website functionality, performance, and user experience. Delivered responsive and efficient websites that met client and company requirements.
Verified Certifications
& Technical Training
Industry-recognized certifications and specialized coursework across offensive security, red team operations, network infrastructure, and cybersecurity operations.
Certified Red Team Operations Management (CRTOM)
- [+] Gained practical understanding of designing and managing enterprise-level red team operations.
- [+] Learned to plan and execute threat-led penetration testing (TLPT / TIBER-EU) engagements
- [+] Gained exposure to C2 architecture design and governance
- [+] Learned approaches for cloud red teaming and validating detection capabilities
SLYSC/Cybersecurity Essentials/2021-B-01
- [+] Gained strong understanding of the CIA Triad and core cybersecurity principles.
- [+] Studied offensive techniques like malware, social engineering, and data exfiltration.
- [+] Acquired hands-on skills in network security, firewalls, IDS/IPS, encryption, and security governance.
- [+] Learned threat intelligence, vulnerability management, and incident response.
- [+] Demonstrated proficiency through Cisco Networking Academy final exam on secure network design.
Networking Essentials
- [+] Designed and implemented SOHO networks with wired and wireless components.
- [+] Configured Cisco routers and switches using CLI.
- [+] Managed network services including DHCP, IPv4/IPv6, and basic wireless LAN setups.
- [+] Completed 19 labs and 24 Packet Tracer exercises for hands-on practice.
- [+] Learned core networking concepts: Ethernet, protocols, basic security, and device communication.
Introduction to Cybersecurity
- [+] Built a foundation in cybersecurity principles, privacy, and data protection.
- [+] Explored global cyber threats and industry demand for cybersecurity skills.
- [+] Learned to identify network vulnerabilities and basic threat defense techniques.
- [+] Studied cybersecurity frameworks, certifications, and career pathways.
- [+] Completed the course and passed the Cisco Networking Academy final exam.
Introduction to IOT
- [+] Gained foundational knowledge of IoT and its role in digital transformation.
- [+] Explored integration of AI/ML, data analytics, and cloud with IoT for intelligent systems.
- [+] Learned the importance of IoT cybersecurity and securing connected devices.
- [+] Studied Intent-Based Networking (IBN) for scalable, automated IoT management.
- [+] Completed Cisco course and passed the final assessment.
NetEgress
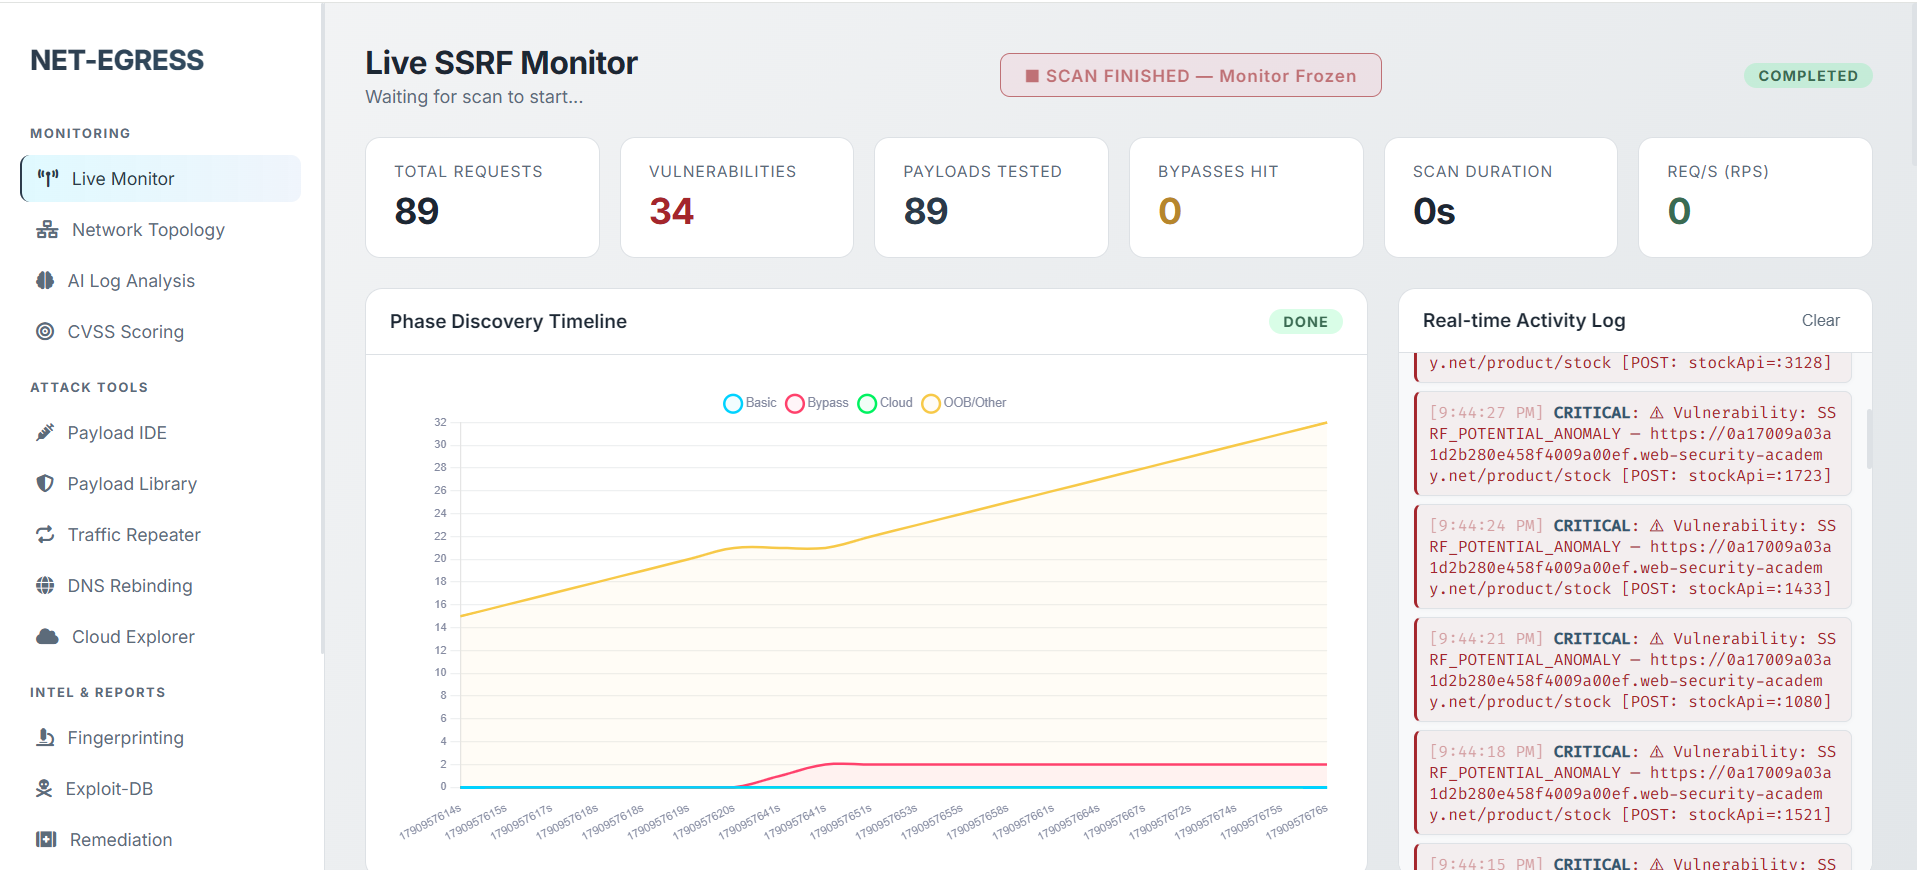
A high-performance, asynchronous Python security tool engineered to detect, assess, and mitigate SSRF (Server-Side Request Forgery) vulnerabilities. Features an async engine powered by aiohttp, statistical baseline anomaly detection, 10 specialized attack phases including cloud metadata exploitation, OOB interaction verification, and multi-format reporting with a real-time web dashboard.
Attack Vectors
10 Attack Phases
Cloud Metadata, DNS Rebinding, CRLF, XXE & Local IPs
Architecture
AsyncIO & aiohttp
High-speed concurrency with adaptive RPS throttling
Detection Core
Smart Baseline Probes
Status code, MD5 hash, response size & timing anomalies
Reporting & UI
HTML, JSON, CSV & Web GUI
Interactive executive reports & Flask SocketIO dashboard
01 / 06
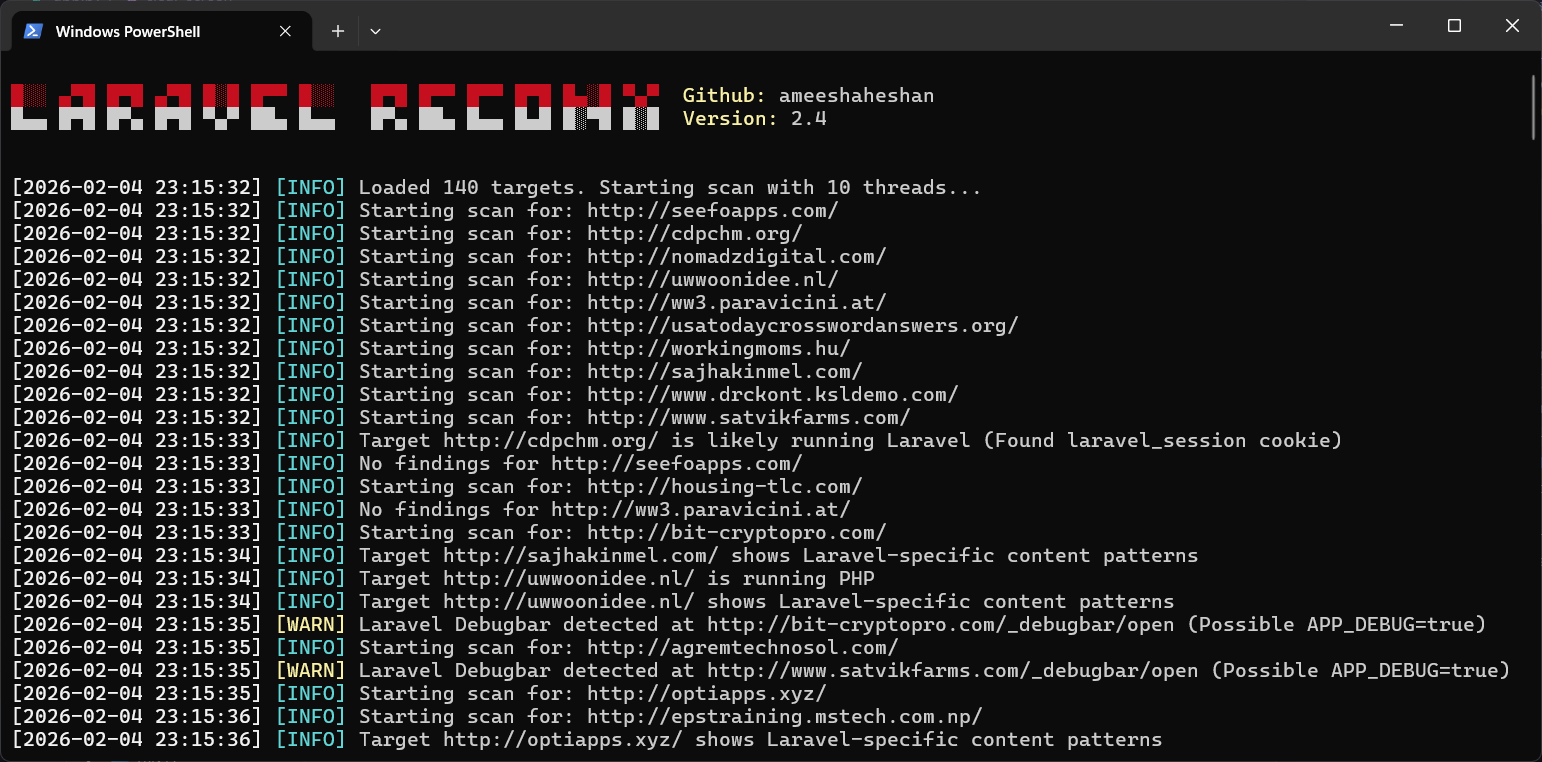
LaravelReconX v2.4
The Ultimate Laravel Reconnaissance & Security Auditing Framework. Engineered for penetration testers and researchers to audit Laravel applications via deep heuristic analysis, verifying exposures of sensitive data (.env files, logs), hunting hidden administrative surfaces, and automating critical CVE and misconfiguration discovery through a multi-threaded CLI and modern dark-themed GUI.
Heuristic Recon
Deep Fingerprinting
Version detection via cookies, headers, localization & asset hashing
Surface Discovery
Admin & Dev Tool Hunter
Nova, Filament, Backpack, Orchid, Telescope & Horizon enumeration
Vulnerability Checks
Logs & CVE Verification
Exposed laravel.log secrets, PHPUnit RCE & installed.json leaks
Architecture & UI
Multi-Thread CLI & GUI
High-concurrency batch engine, futuristic dark GUI & Blue Team mode
-t 20) alongside a modern dark Kivy GUI, automated Blue Team security checklists, and rich HTML/JSON/CSV reports.
02 / 06
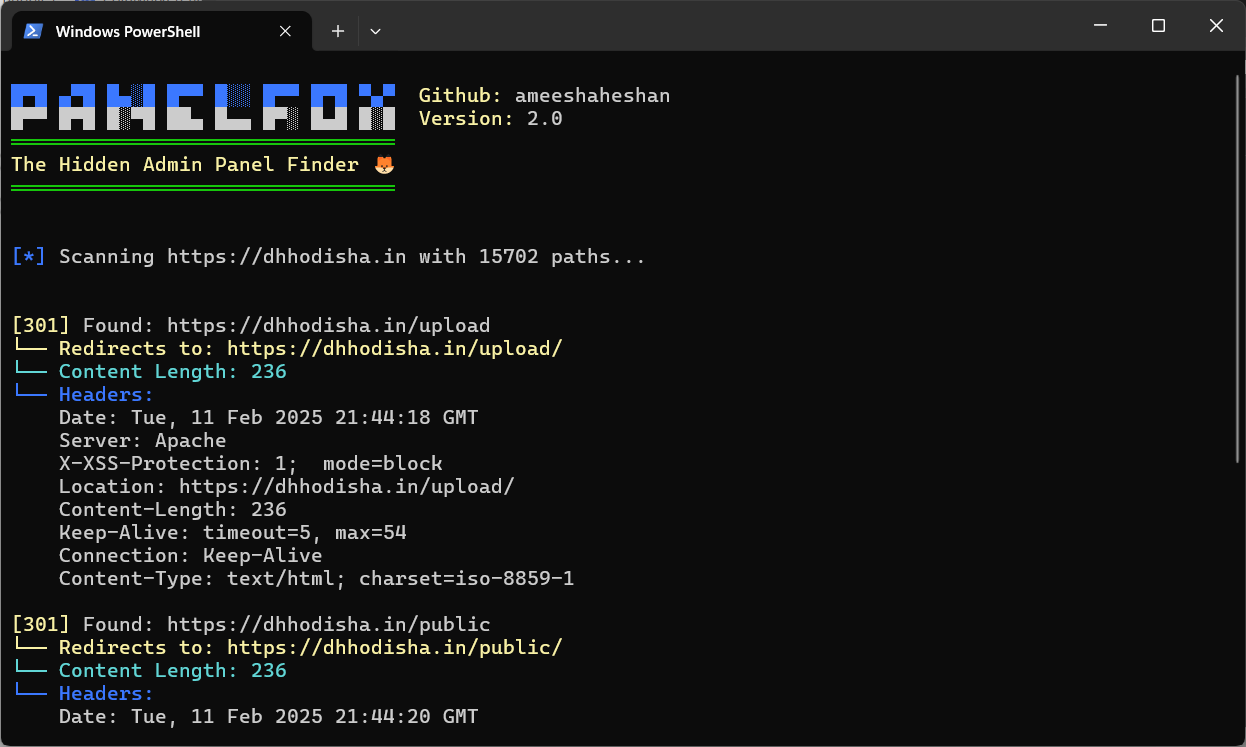
PanelFox
A high-performance Python reconnaissance framework engineered to discover obscure and hidden administrative interfaces in web applications. Features deep URL crawling, smart naming convention heuristics, multi-threading (1–10 threads), HTTP verb tampering, proxy rotation, header injection (e.g. X-Forwarded-For), and User-Agent rotation for stealthy penetration testing.
Recon Engine
Deep Path Crawling
Targeted dictionary fuzzing & smart naming convention matching
Method & Headers
HTTP Verb Tampering
GET, POST, HEAD, PUT, DELETE with custom header & cookie injection
Evasion & Stealth
Proxy & UA Rotation
Upstream proxy chaining, randomized User-Agents & delay throttling
Analysis Core
Response & Status Filter
HTTP status code filtering, raw response logging & SSL bypass support
X-Forwarded-For), rotates User-Agent lists, supports proxy routing (-p), and switches between 5 HTTP verbs.
-I), and response dumps.
03 / 06
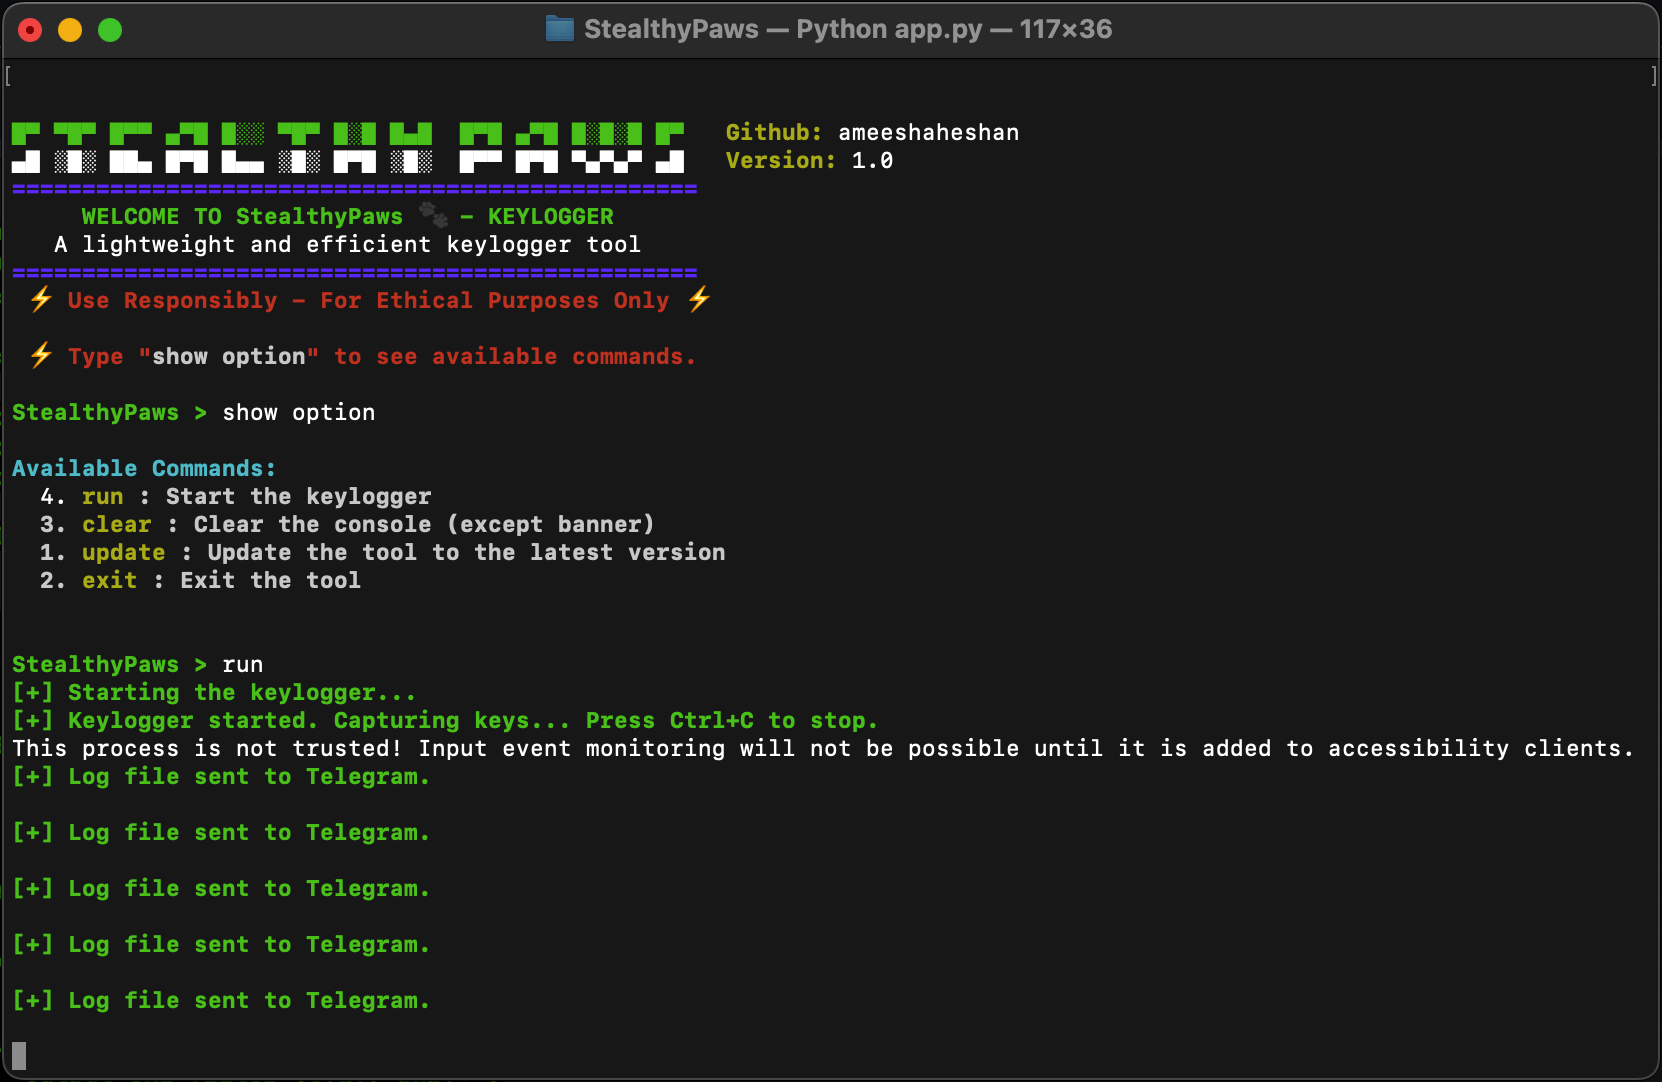
StealthyPaws
A cross-platform Python security research framework engineered for low-level input monitoring, keystroke telemetry, and automated remote log exfiltration. Developed for authorized security assessments and ethical penetration testing, it features consoleless background daemon execution, real-time Telegram Bot API telemetry dispatch, interactive CLI controls, and standalone binary packaging via PyInstaller.
Input Telemetry
Keystroke Logging
Low-level event capture including functional keys, enter & modifiers
C2 & Telemetry
Telegram Bot API
Encrypted automated dispatch of timestamped audit logs every 30s
Process Stealth
Silent Daemon
Consoleless background execution & standalone PyInstaller compilation
Architecture
Cross-Platform CLI
Interactive runtime commands (run, clear, update) on Win/Linux/macOS
04 / 06
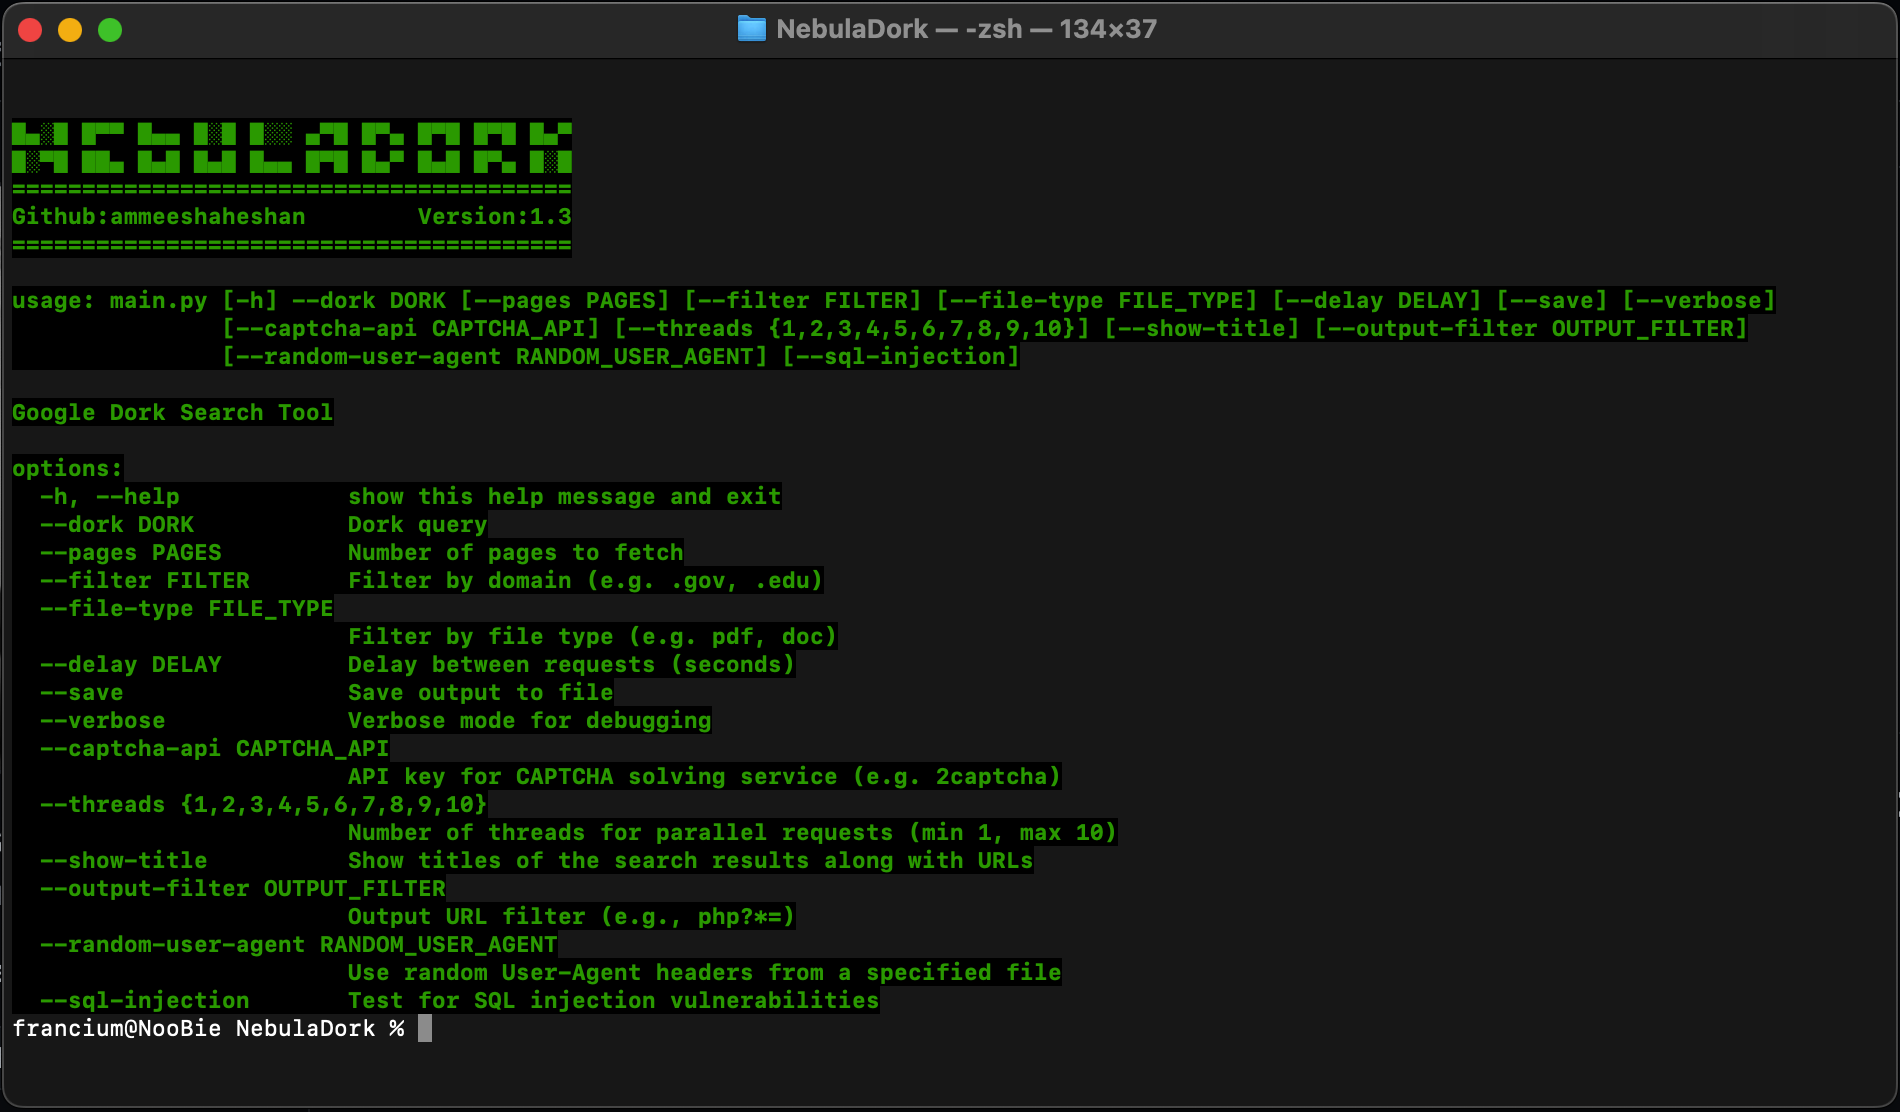
NebulaDork
An open-source, high-speed Python framework engineered for automated Google dorking, passive OSINT reconnaissance, and active SQL injection vulnerability assessment. Features multi-threaded parallel query execution (1–10 threads), automated 2Captcha solving support, targeted domain (.gov, .edu) and filetype filtering, randomized User-Agent header rotation, and integrated SQLi vulnerability verification with customizable output logging.
Recon Engine
Multi-Thread Dorking
Parallel Google search execution with 1–10 configurable worker threads
Vulnerability Core
Automated SQLi Testing
Integrated payload fuzzing & error analysis for SQL-vulnerable endpoints
Evasion & Bypass
CAPTCHA & UA Rotation
2Captcha API integration, request delay throttling & randomized User-Agents
Target Filtering
Domain & Filetype Filters
Granular search filtering by TLD (.gov, .edu), file extensions & URL patterns
05 / 06
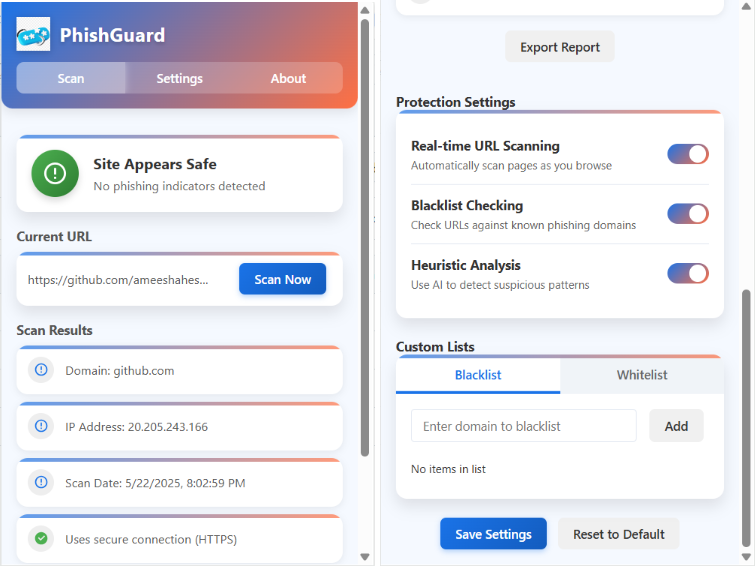
PhishGuard
A modern, feature-rich Chrome security extension engineered for real-time anti-phishing defense and malicious website detection. Combines active in-page DOM heuristics, WhoAPI domain age verification, Cloudflare DNS-over-HTTPS IP resolution, SSL certificate validation, hidden credential form detection, and customizable domain blacklists with a sleek popup UI and exportable security audit reports.
Detection Core
Heuristic & DOM Analysis
Suspicious keywords, excessive subdomains, redirect chains & hidden form fields
Reputation Intel
Domain Age & DoH Lookup
WhoAPI registration age verification & Cloudflare 1.1.1.1 DNS resolution
Active Protection
Real-Time URL Scanning
Instant page analysis, context menu right-click scans & SSL status checks
Custom Rules & UI
Rule Engine & Reports
Custom blacklist/whitelist controls, responsive popup & exportable audit logs
06 / 06
AI Security Consulting & Secure AI Integration
Comprehensive AI security audits and advisory services for integrating artificial intelligence safely into production. Safeguarding machine learning pipelines, LLM deployments, and enterprise applications against prompt injection, model poisoning, data exfiltration, and algorithmic vulnerabilities with robust alignment and compliance standards.
Web Application Security
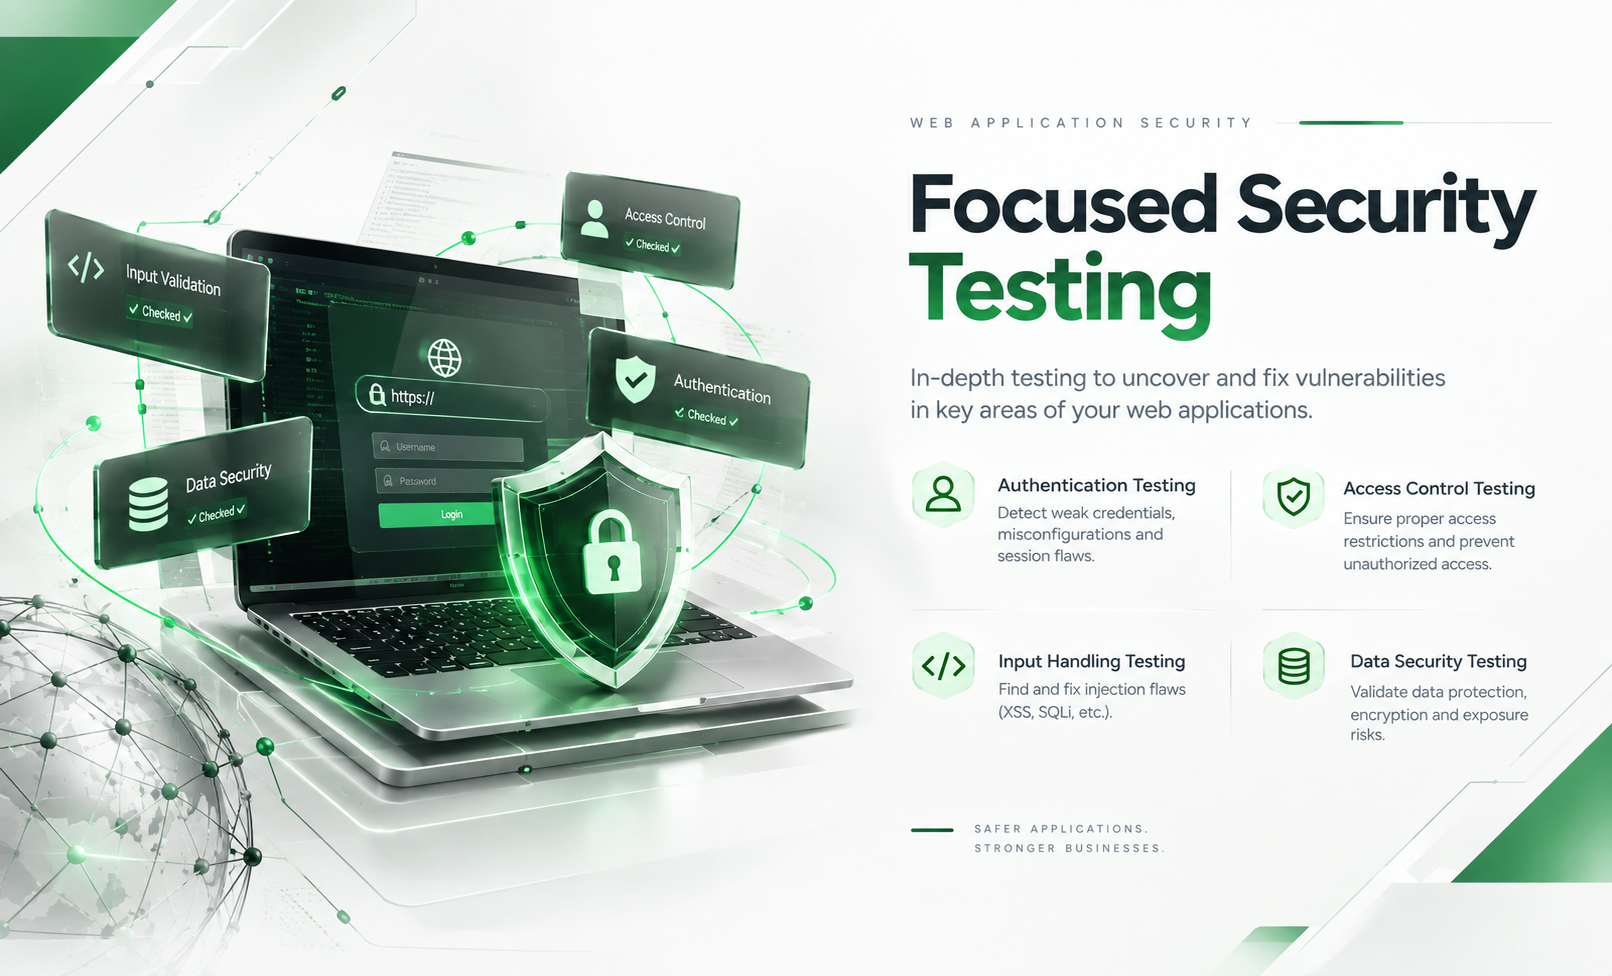
In-depth web application security evaluations targeting critical vulnerabilities across frontend, backend, and API layers. Identifying authentication flaws, business logic weaknesses, injection exploits, and authorization bypasses while delivering prioritized remediation strategies to fortify your web infrastructure.
Penetration Testing
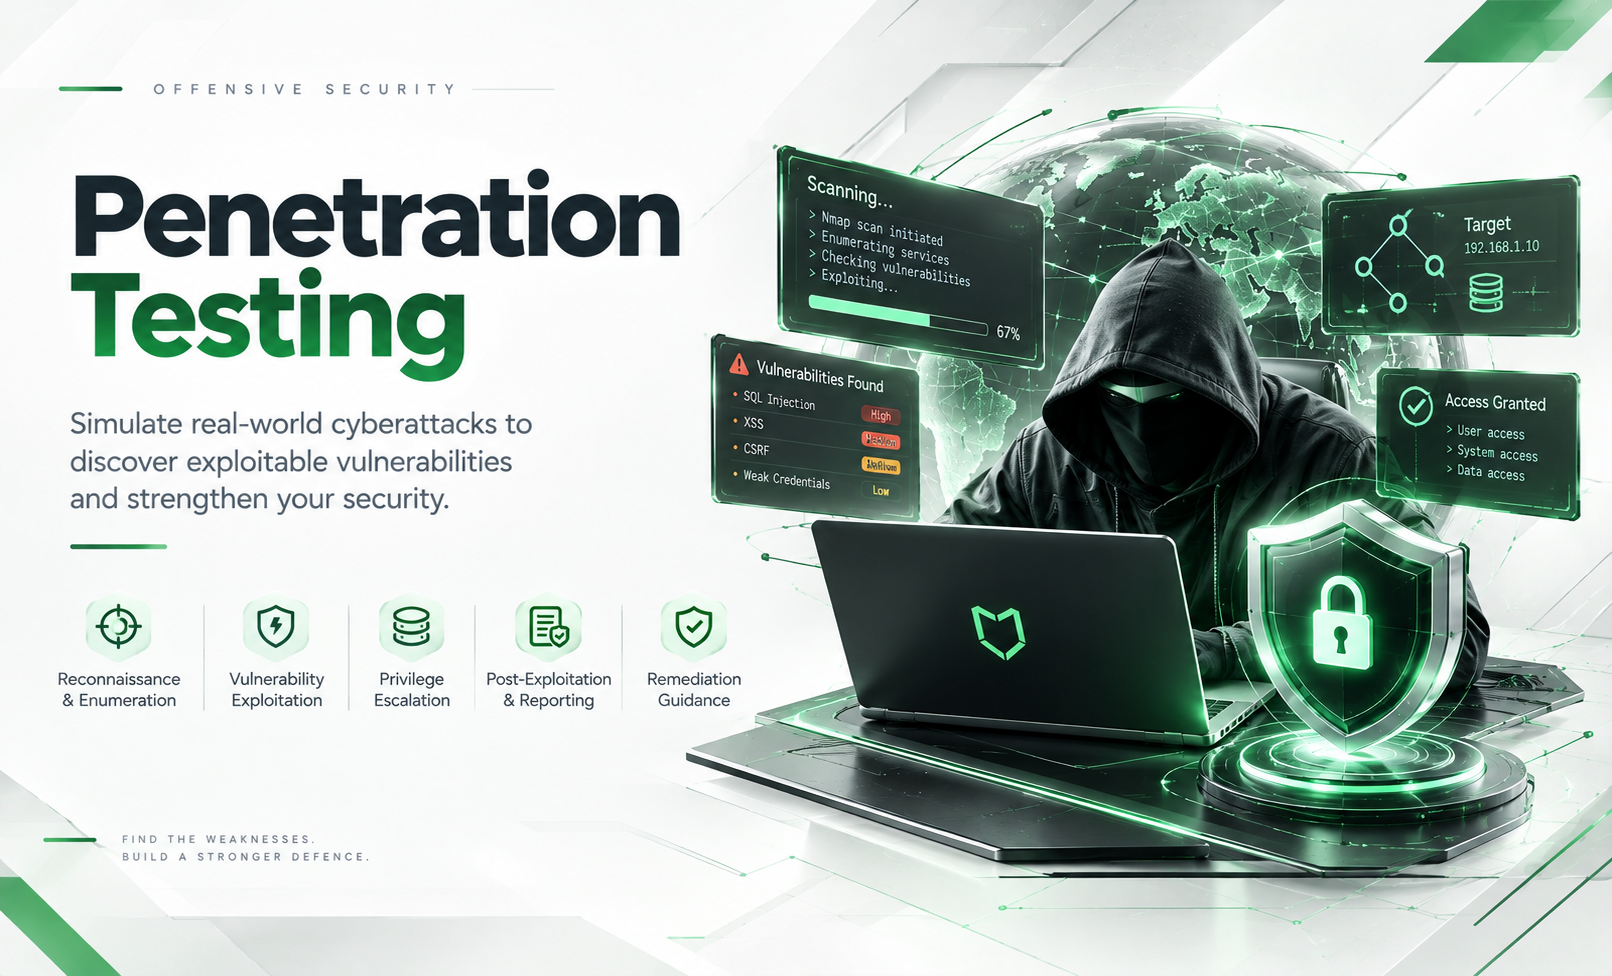
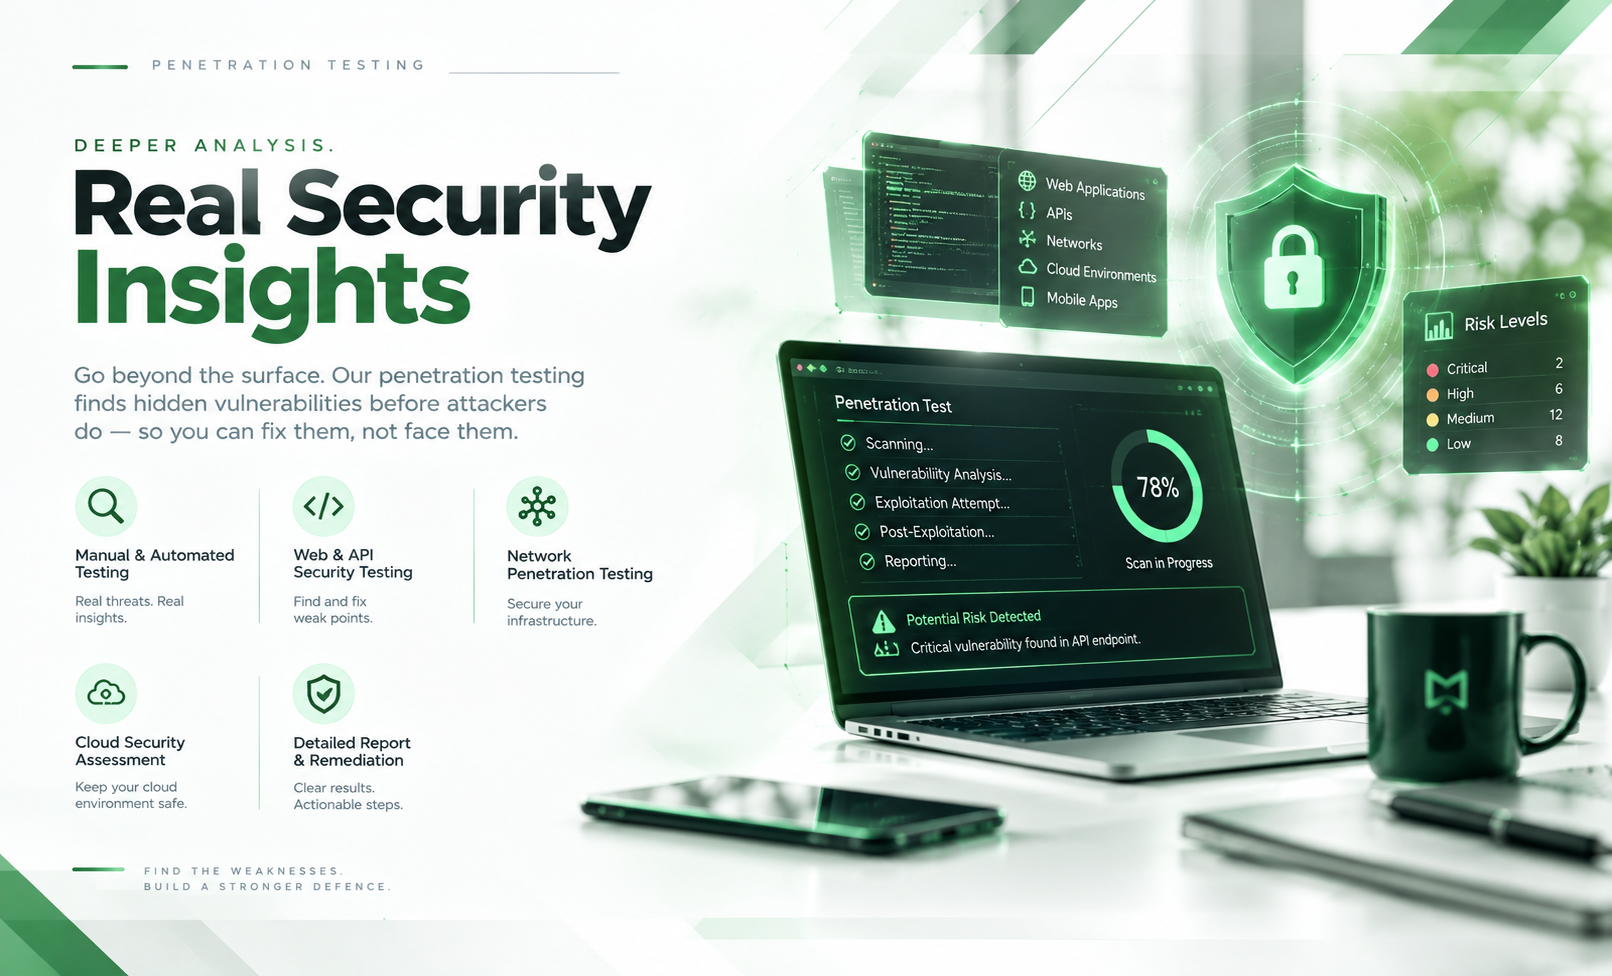
Simulated real-world cyberattacks designed to uncover exploitable flaws across networks, hosts, and internal systems before malicious adversaries do. Combining deep manual testing with custom offensive tooling to assess perimeter defenses, escalate privileges, and provide clear executive remediation roadmaps.
Malware & Threat Investigation
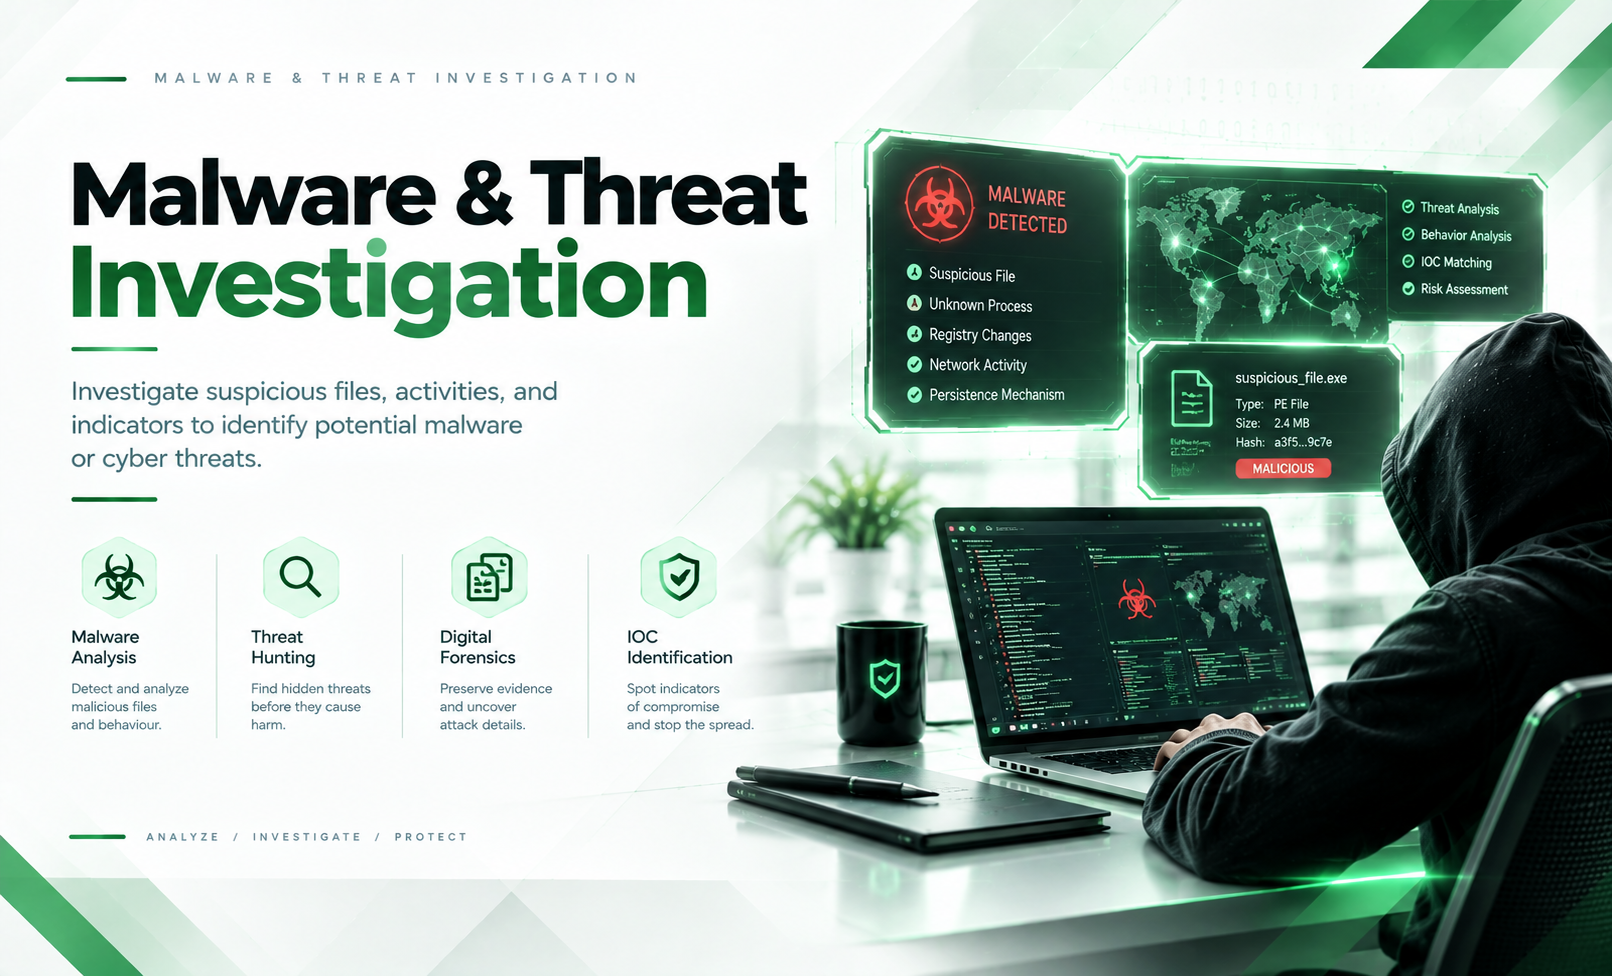
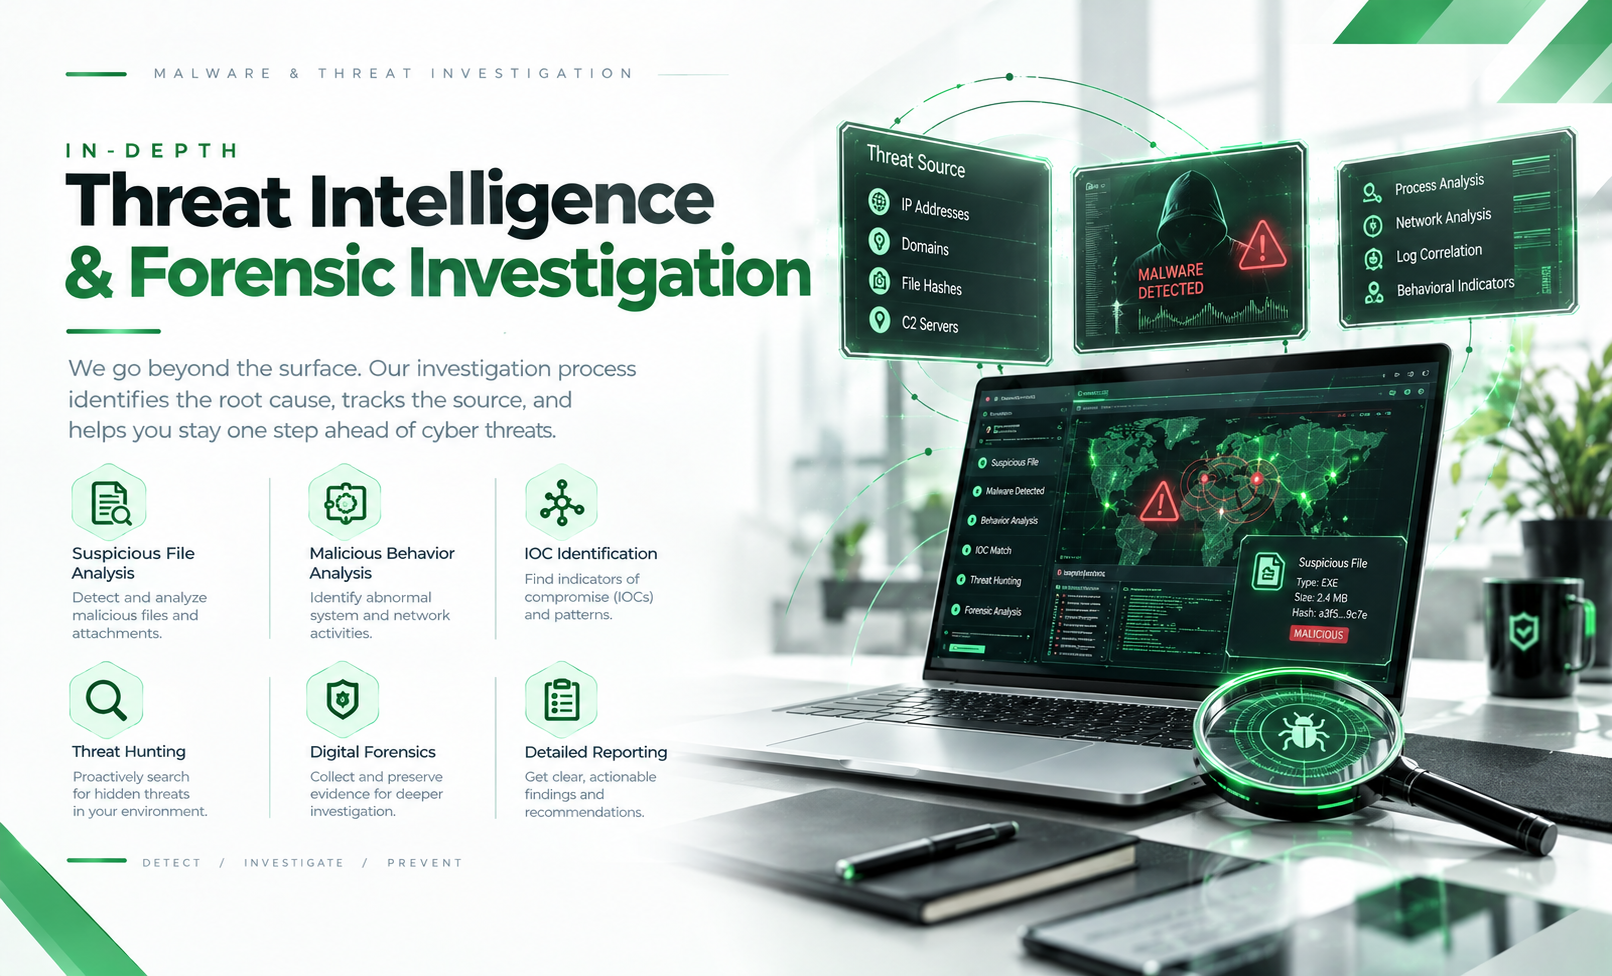
In-depth malware dissection, static and dynamic payload analysis, and root-cause threat investigations. Identifying indicators of compromise (IOCs), analyzing malicious behavior, tracking adversary attack vectors, and supporting incident response teams to rapidly neutralize persistent cyber threats.
Cloud Security Assessment
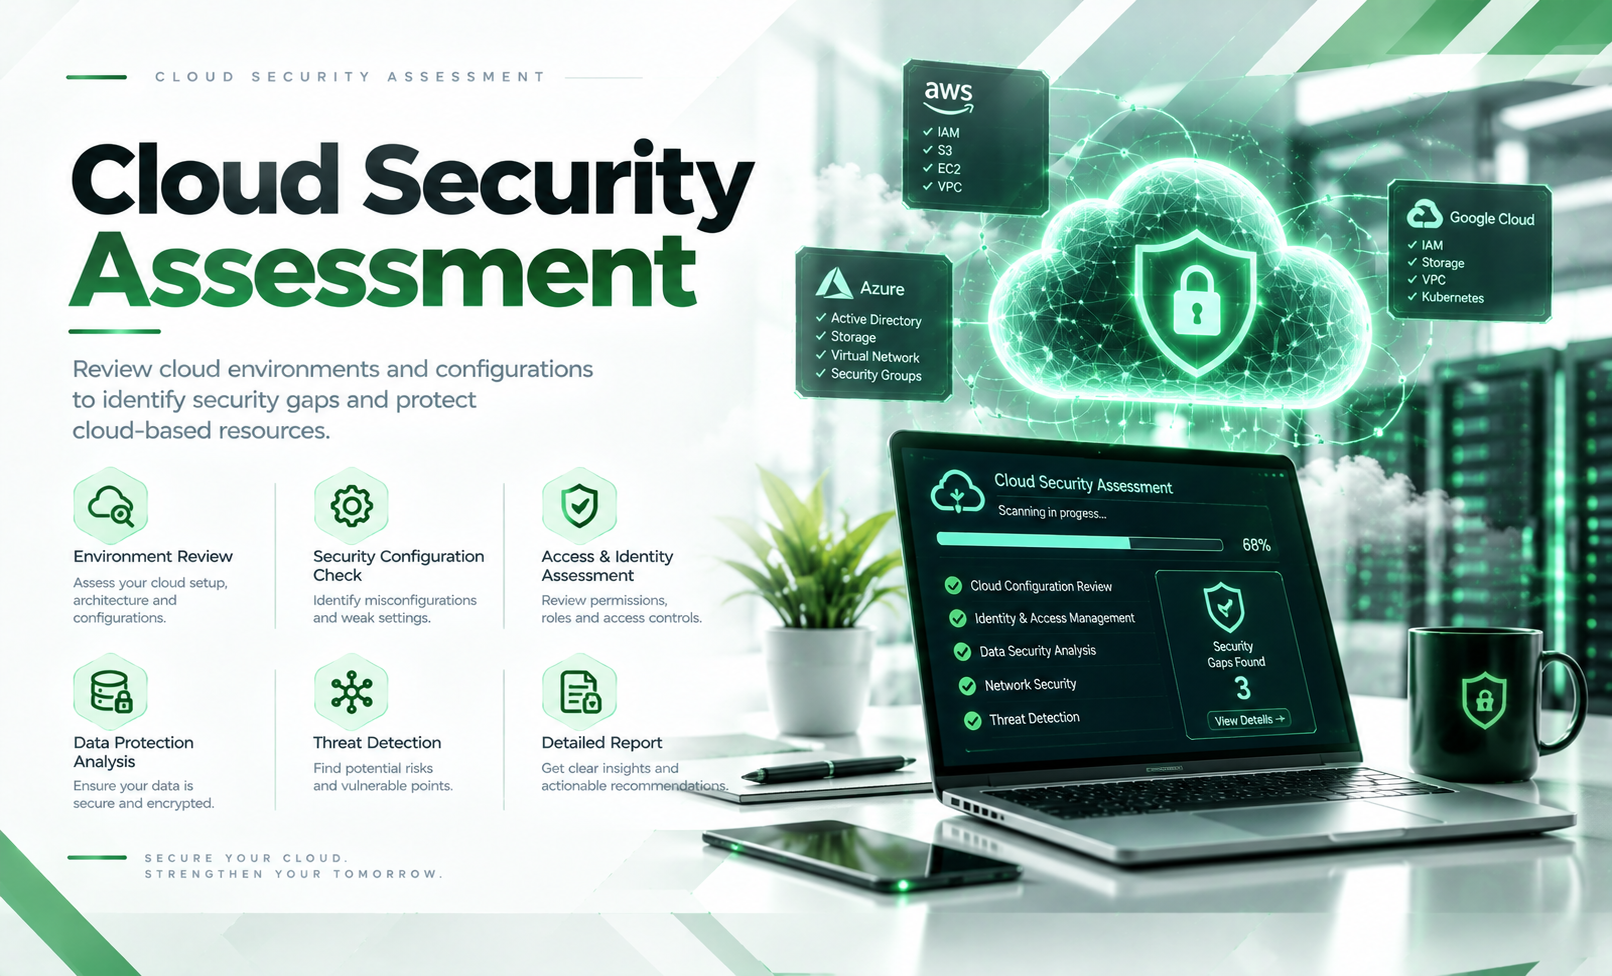
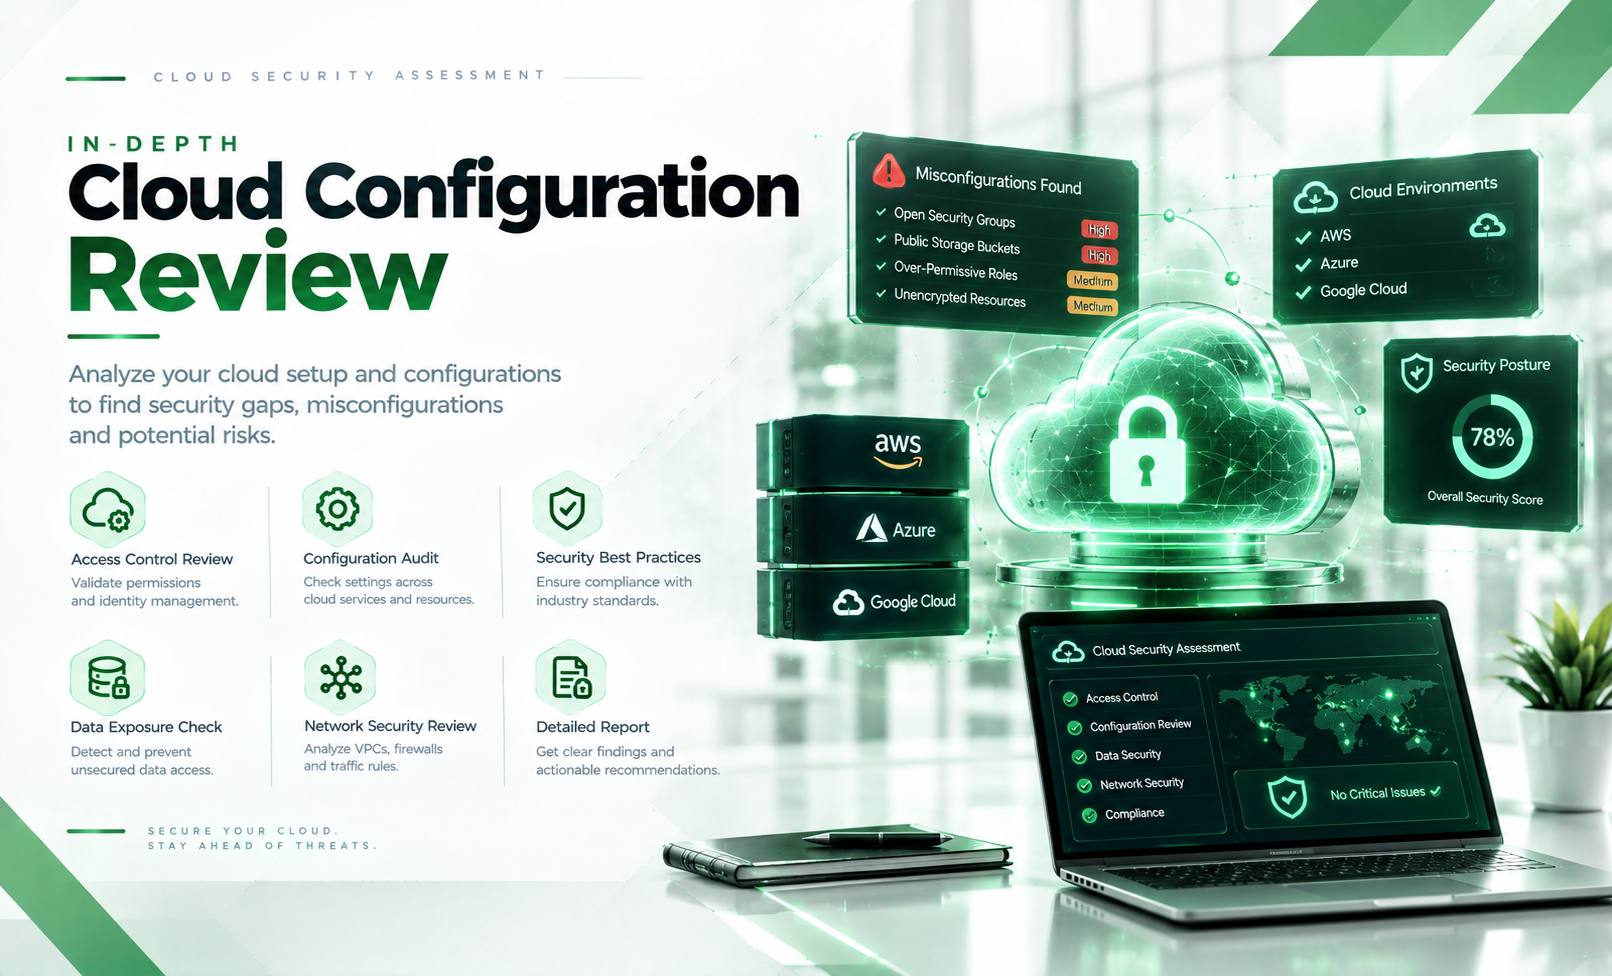
Detailed cloud posture reviews across AWS, Microsoft Azure, and Google Cloud environments. Auditing IAM policies, network security groups, container orchestrations, and cloud storage configurations to eliminate misconfigurations, prevent data leaks, and ensure compliance with CIS and regulatory benchmarks.
AI & Automation
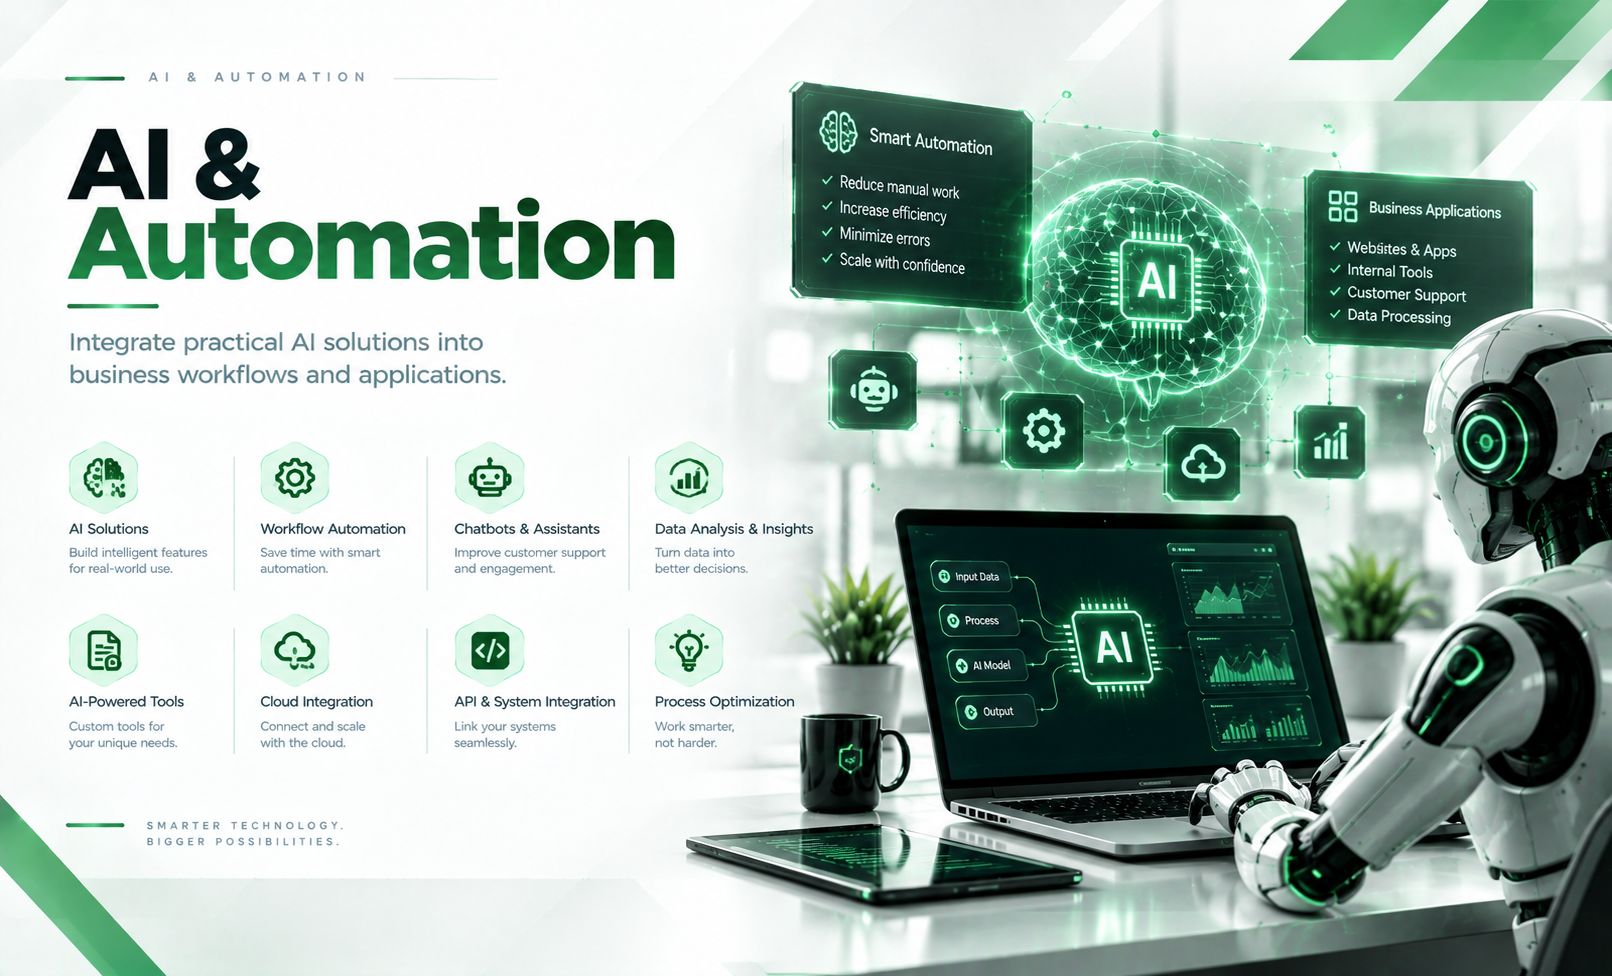
Designing and deploying tailor-made artificial intelligence workflows, autonomous agents, and smart automations. Accelerating operational velocity through state-of-the-art LLM fine-tuning, intelligent API integrations, and scalable Python automation pipelines tailored to specific industry demands.
Business Process Automation
Transforming manual, repetitive business operations into automated, resilient digital pipelines. Leveraging modern scripting, API connectors, and automated monitoring to reduce operational latency, eliminate human error, synchronize multi-platform data, and optimize organizational productivity.
E-commerce Technology Consulting
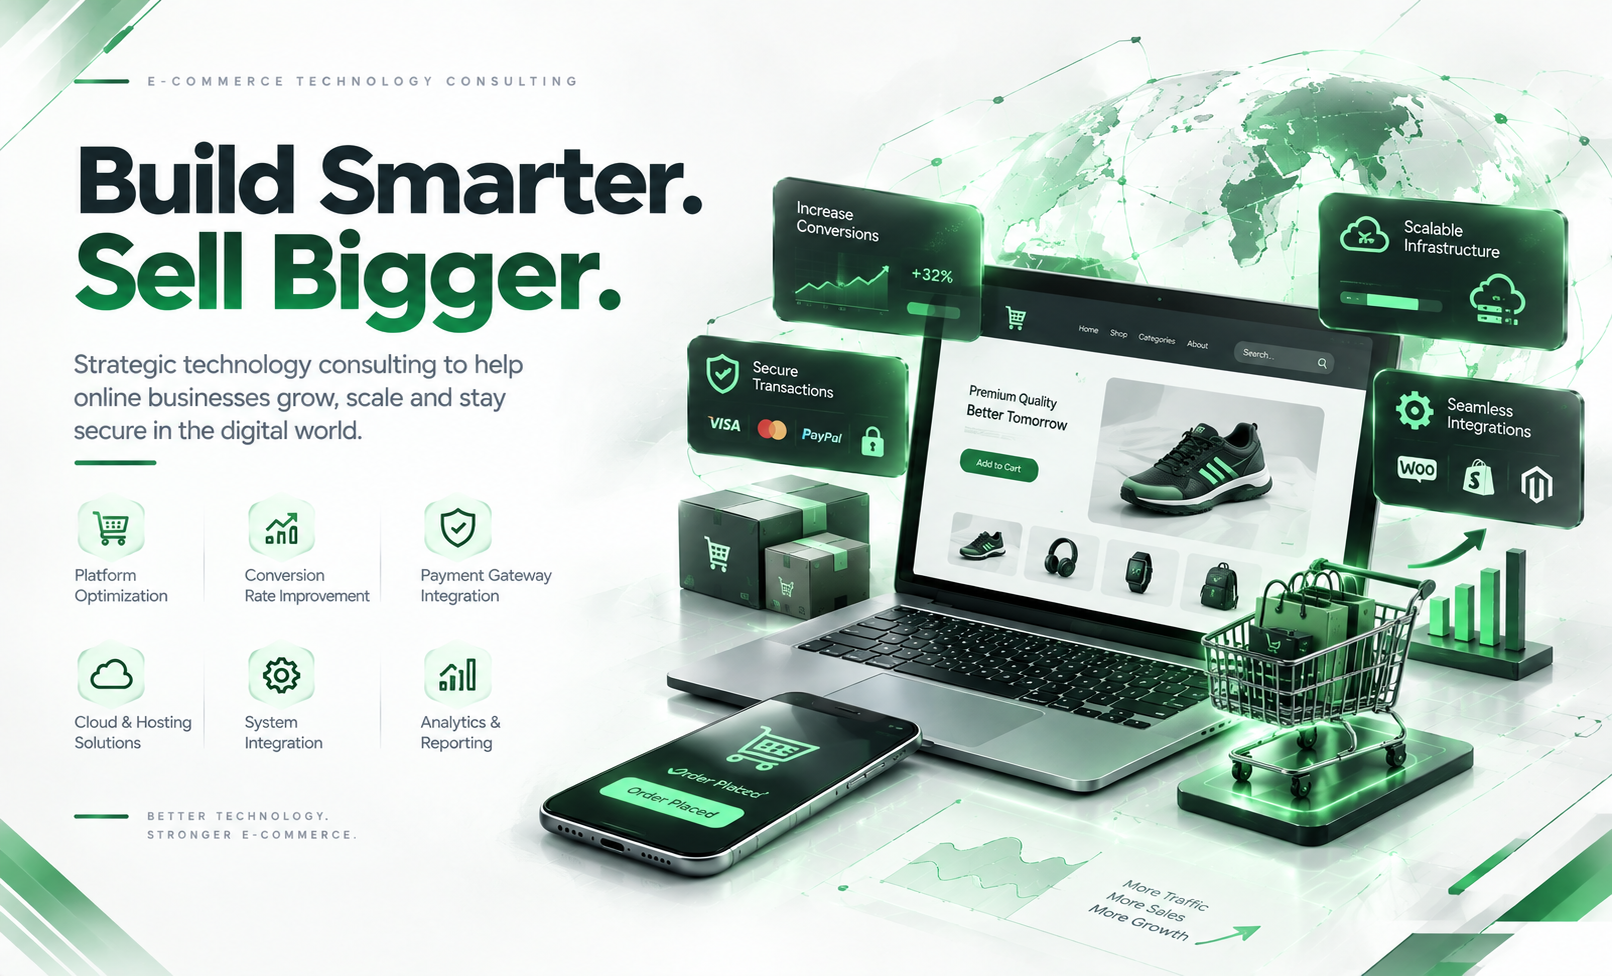
Strategic architectural and technical advisory for modern online storefronts, headless e-commerce stacks, and payment systems. Optimizing checkout security, transaction integrity, server scalability, and site load speeds to maximize uptime, enhance conversion rates, and protect consumer financial transactions.
Enterprise Level Security
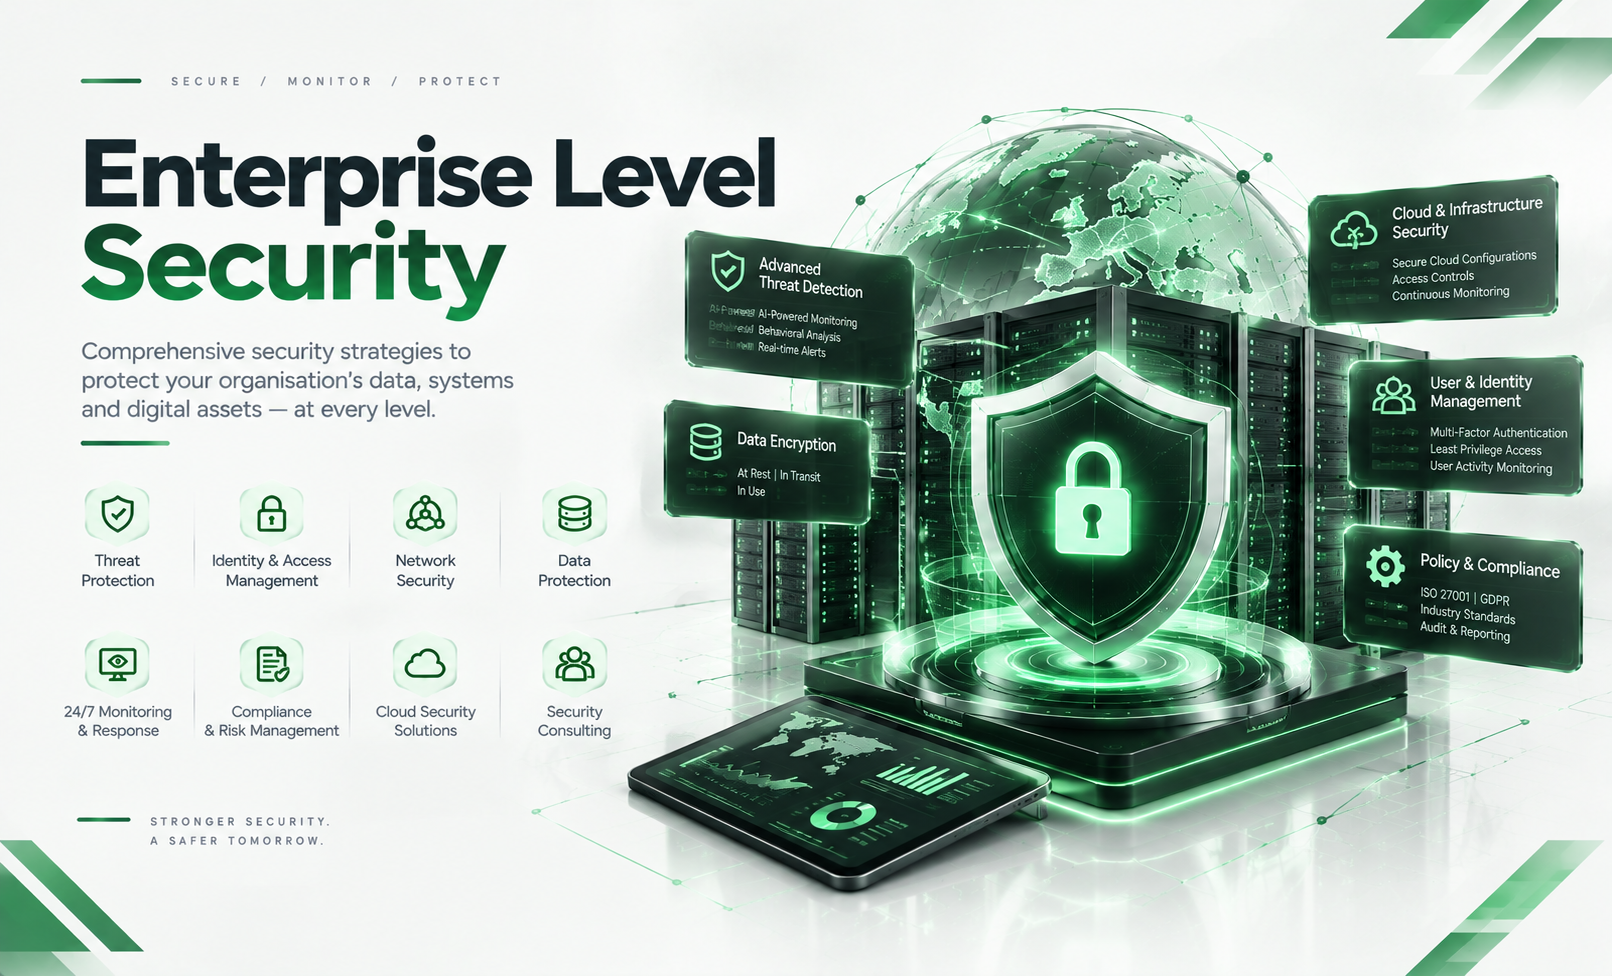
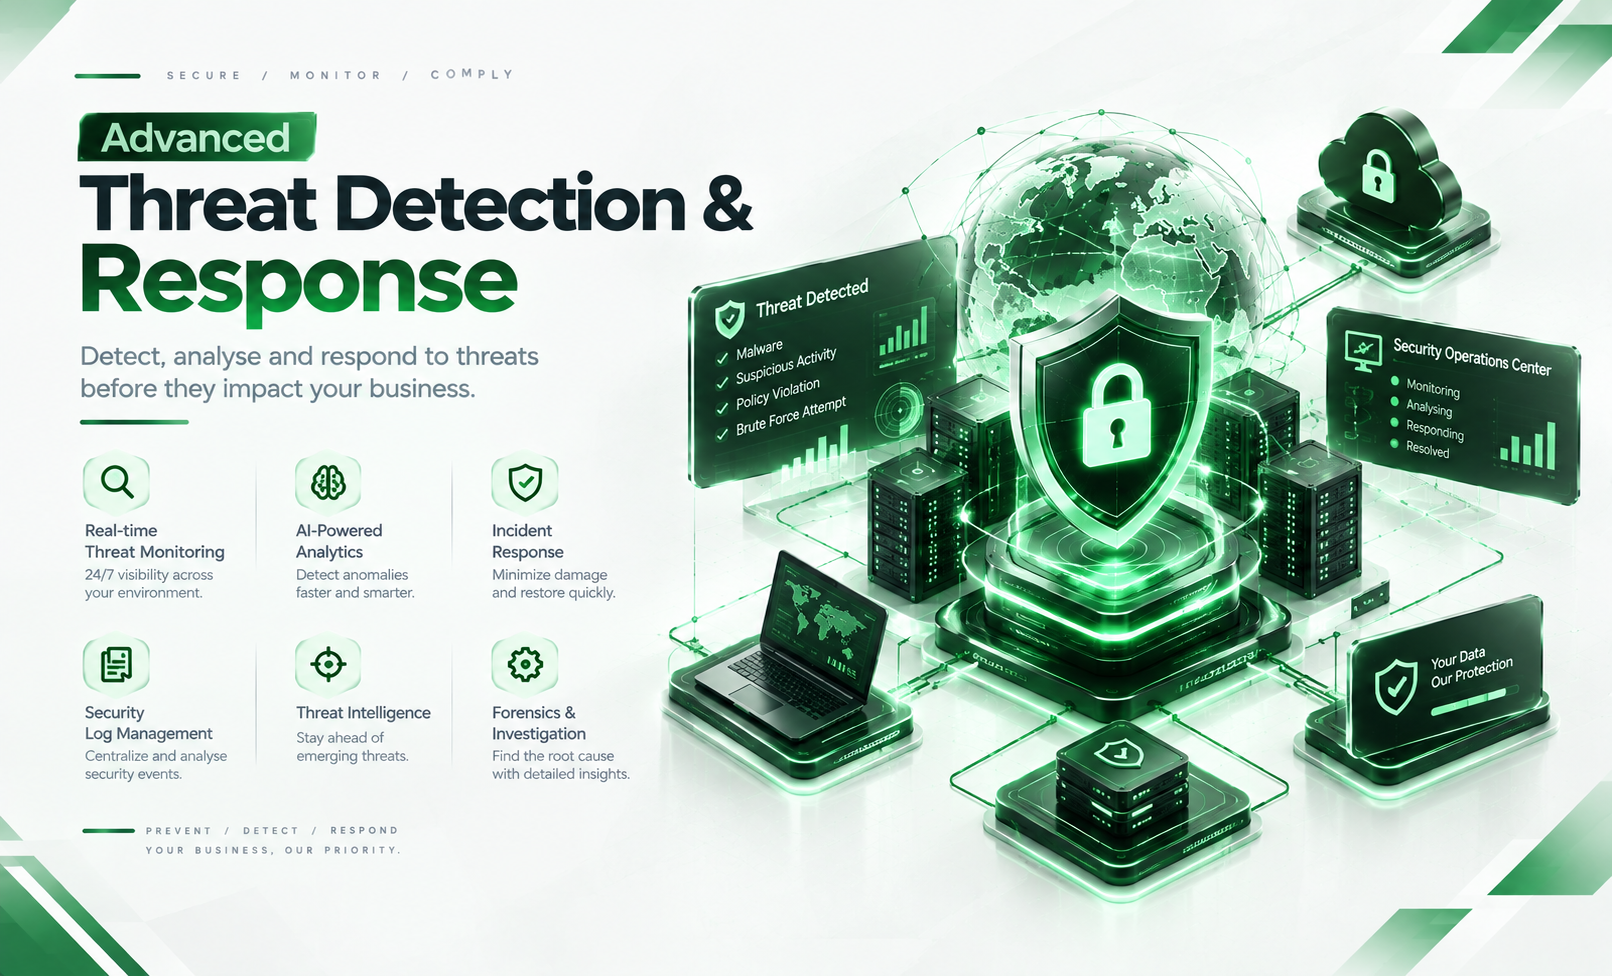
Holistic enterprise security advisory and defense-in-depth implementations designed for high-scale organizations. Establishing Zero Trust frameworks, robust SOC monitoring, centralized access governance, and strict compliance postures to safeguard mission-critical assets against sophisticated nation-state and cybercrime syndicates.
Tools, languages and security environments
engineered for offensive & defensive research
A comprehensive index of programming languages, offensive vulnerability assessment tools, cloud security analyzers, and operational defense systems utilized across active penetration testing and security research engagements.
Primary language for automated vulnerability scanners, telemetry daemons, SSRF engines & custom security tooling.
High-concurrency network scanners, fast TCP/HTTP probes, multithreaded recon utilities & static binaries.
Linux system automation, offensive command pipelines, environment setup & automated recon workflows.
Enterprise framework auditing, heuristic exposure checks, auth mechanism verification & CVE hunting.
Source code auditing, web application vulnerability analysis, deserialization vectors & auth bypass testing.
Relational database internals, structured queries, SQL injection payload crafting & data extraction testing.
Application security reviews, enterprise backend code analysis, object deserialization & endpoint assessment.
Web Application Testing
OWASP Top 10 auditing, business logic flaw identification, API endpoint fuzzing, request tampering & session security testing.
Vulnerability Assessment
Infrastructure vulnerability scanning, CVE enumeration, exposed service discovery, configuration flaw analysis & security patching audits.
Vulnerability Exploitation
Controlled proof-of-concept verification, automated vulnerability weaponization, payload delivery & custom exploit tooling.
Bug Bounty Hunting
Large-scale reconnaissance, wild-card subdomain enumeration, parameter extraction, asset discovery & high-volume web probing.
Cloud Security
Multi-cloud security posture management, IAM privilege escalation audits, S3/blob bucket exposure testing & baseline compliance.
Network Monitoring
Deep packet capture analysis, network protocol examination, MITM vector assessment, rogue node detection & anomaly tracking.
Security Auditing
Automated security compliance verification (CIS benchmarks), host hardening baselines, configuration auditing & IT inventory control.
Security Operations (SOC) Basics
Real-time security telemetry, operational metric dashboards, alert threshold configurations & log aggregation visualization.
Risk Assessment & Management
Threat landscape evaluation, asset risk exposure scoring, business impact analysis & remediation prioritization workflows.
Incident Response Basics
Digital forensics triage, host artifact acquisition, filesystem examination, attack timeline reconstruction & evidence preservation.
Exploit Development Basics
Binary analysis fundamentals, memory corruption mechanics, stack overflow payload crafting, socket interaction & CTF pwn automation.
What clients
say about me
0 %
Client satisfaction
0 +
Projects completed


Interested in cybersecurity,
security research or technical
collaboration? Get in touch.
“ Security is not a product, but a process. “
All rights reserved
© 2025 Nova Exzzr